Guard AI

AIMS based on ISO/IEC 42001

ISO/IEC 42001 without folders of spreadsheets and e-mails

Guard AI connects AI literacy training with what a company needs to manage AI: who is responsible for what, which AI risks it carries, which measures it takes and how it shows this to an auditor. Everything builds on everything else, so nothing is kept twice.

An AIMS is an AI management system based on ISO/IEC 42001. The SoA (Statement of Applicability) lists the 38 Annex A controls of the standard and states which apply to you and why.

Guard AI helps you prepare and evidence an AIMS; it is not a certification.

ISO/IEC 42001 AIMS checklist in the admin panel

What an AIMS does for your company

Trust of customers and partners

Show that you use AI in a managed way: with rules, responsible people and assessed risks. Useful in tenders and supplier questionnaires.

Ready for an audit

The structure is organised along clauses 4 to 10 and Annex A of the standard. The auditor gets clear outputs instead of a folder of e-mails.

One system instead of spreadsheets

Risk register, action plan, documents and approvals sit in one place and refer to each other. The SoA links straight to the policy, inventory, training and incidents in Guard AI.

Builds on your training

Training records, policy acknowledgements and incident reports you already keep in Guard AI serve directly as AIMS evidence.

How it fits together

Each step uses the result of the one before. At the end you have the material to show an auditor. The numbers are clauses of ISO/IEC 42001.

  1. 15.3

    Roles and responsibilities

    Name an AIMS manager and the people responsible for risks, impacts, suppliers and other areas. Employees see them as contacts.

  2. 24.3, A.10

    AI inventory and suppliers

    Record your AI tools and assess their vendors. Risks and actions then refer to those tools.

  3. 36.1.2, 6.1.3

    Risk register

    Risks with likelihood and impact, your own acceptance criterion and management approval of the residual risk.

  4. 46.1.4, 8.4

    Impact assessment

    How an AI system affects people and society, across ten areas from rights to the environment.

  5. 56.1.3

    Statement of Applicability

    The 38 Annex A controls. Activate the ones that apply, with a justification, an owner and links to evidence in Guard AI.

  6. 66.1.1

    Action plan

    Tasks with due dates and owners, e-mail reminders and an effectiveness review. Calendar export.

  7. 77.5

    Documents with approval

    The 16 pieces of documented information the standard asks for. Items Guard AI already records (such as the AI policy) are marked done automatically; you add the rest as a link or text and the responsible person approves it.

  8. 89.1

    Material for the auditor

    The SoA to print or as CSV, documents with a SHA-256 fingerprint and the audit proof pack as PDF.

Running in the background

Training and awareness

Role-based courses, AI policy acknowledgements and certificates evidence competence and awareness.

Incidents and nonconformities

AI incident reports, anonymous ones too, with review and measures form the record of nonconformities.

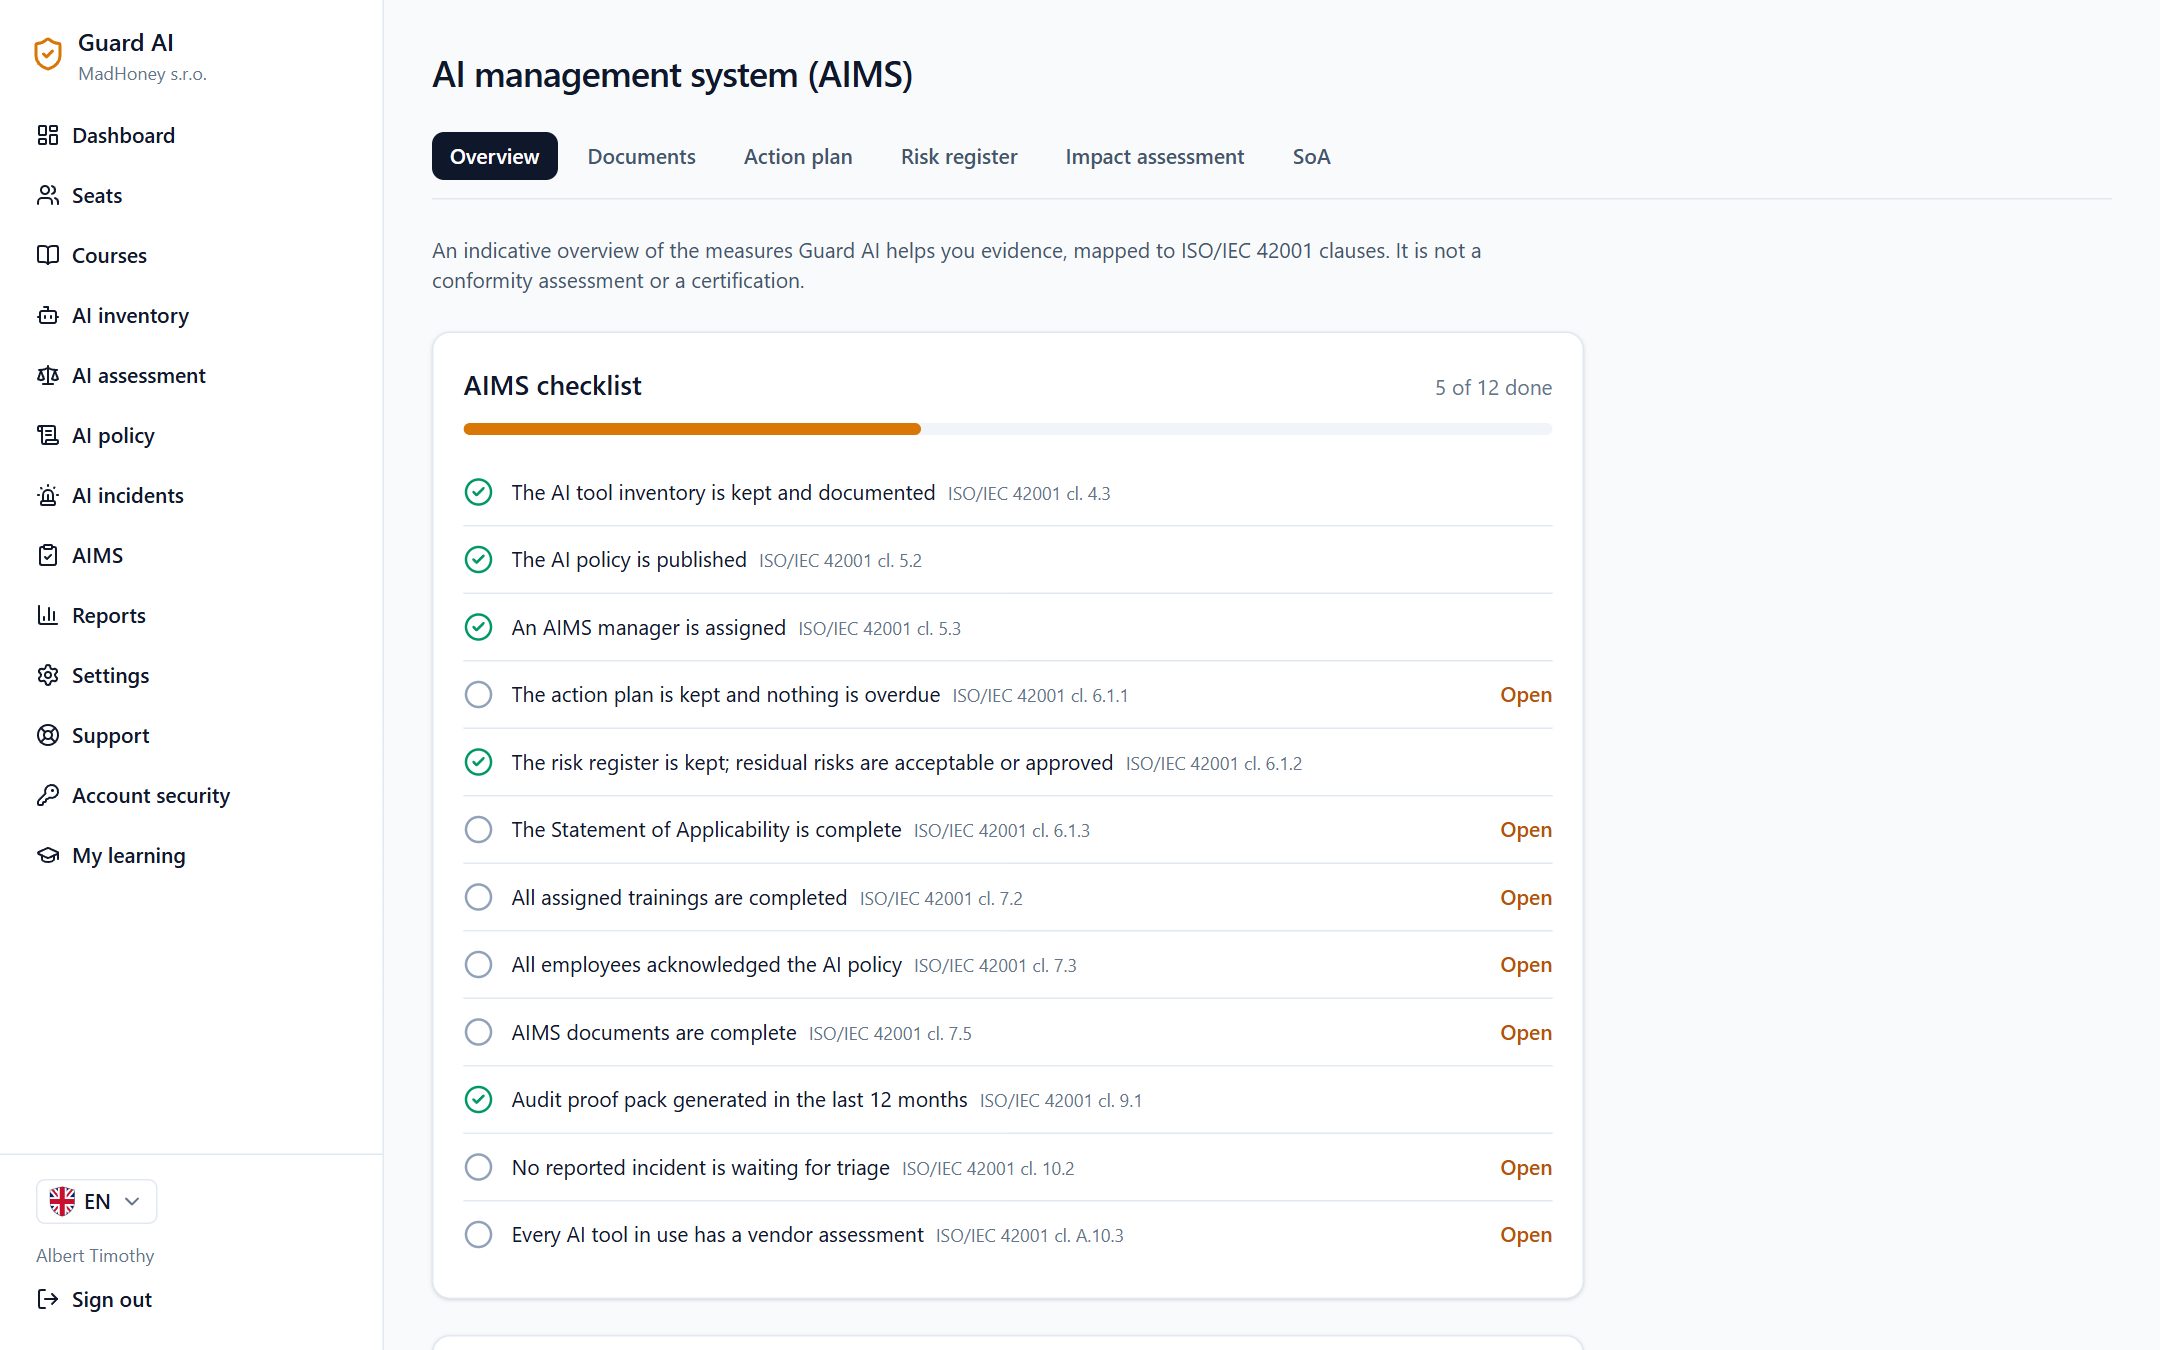
Readiness checklist

The AIMS readiness overview shows what is done and where something is still missing.

What it looks like in the app

Screens from the Guard AI admin panel, shown on a fictional company.

AI management system (AIMS)

An ISO/IEC 42001 checklist built from what you already keep in Guard AI: the inventory, policy, vendor assessments, training and incidents. You see at once what is still missing.

  • In every plan
  • Roles and responsibilities per clause 5.3 with contact people for employees
  • Helps you prepare; it is not a certification
ISO/IEC 42001 AIMS checklist in the admin panel

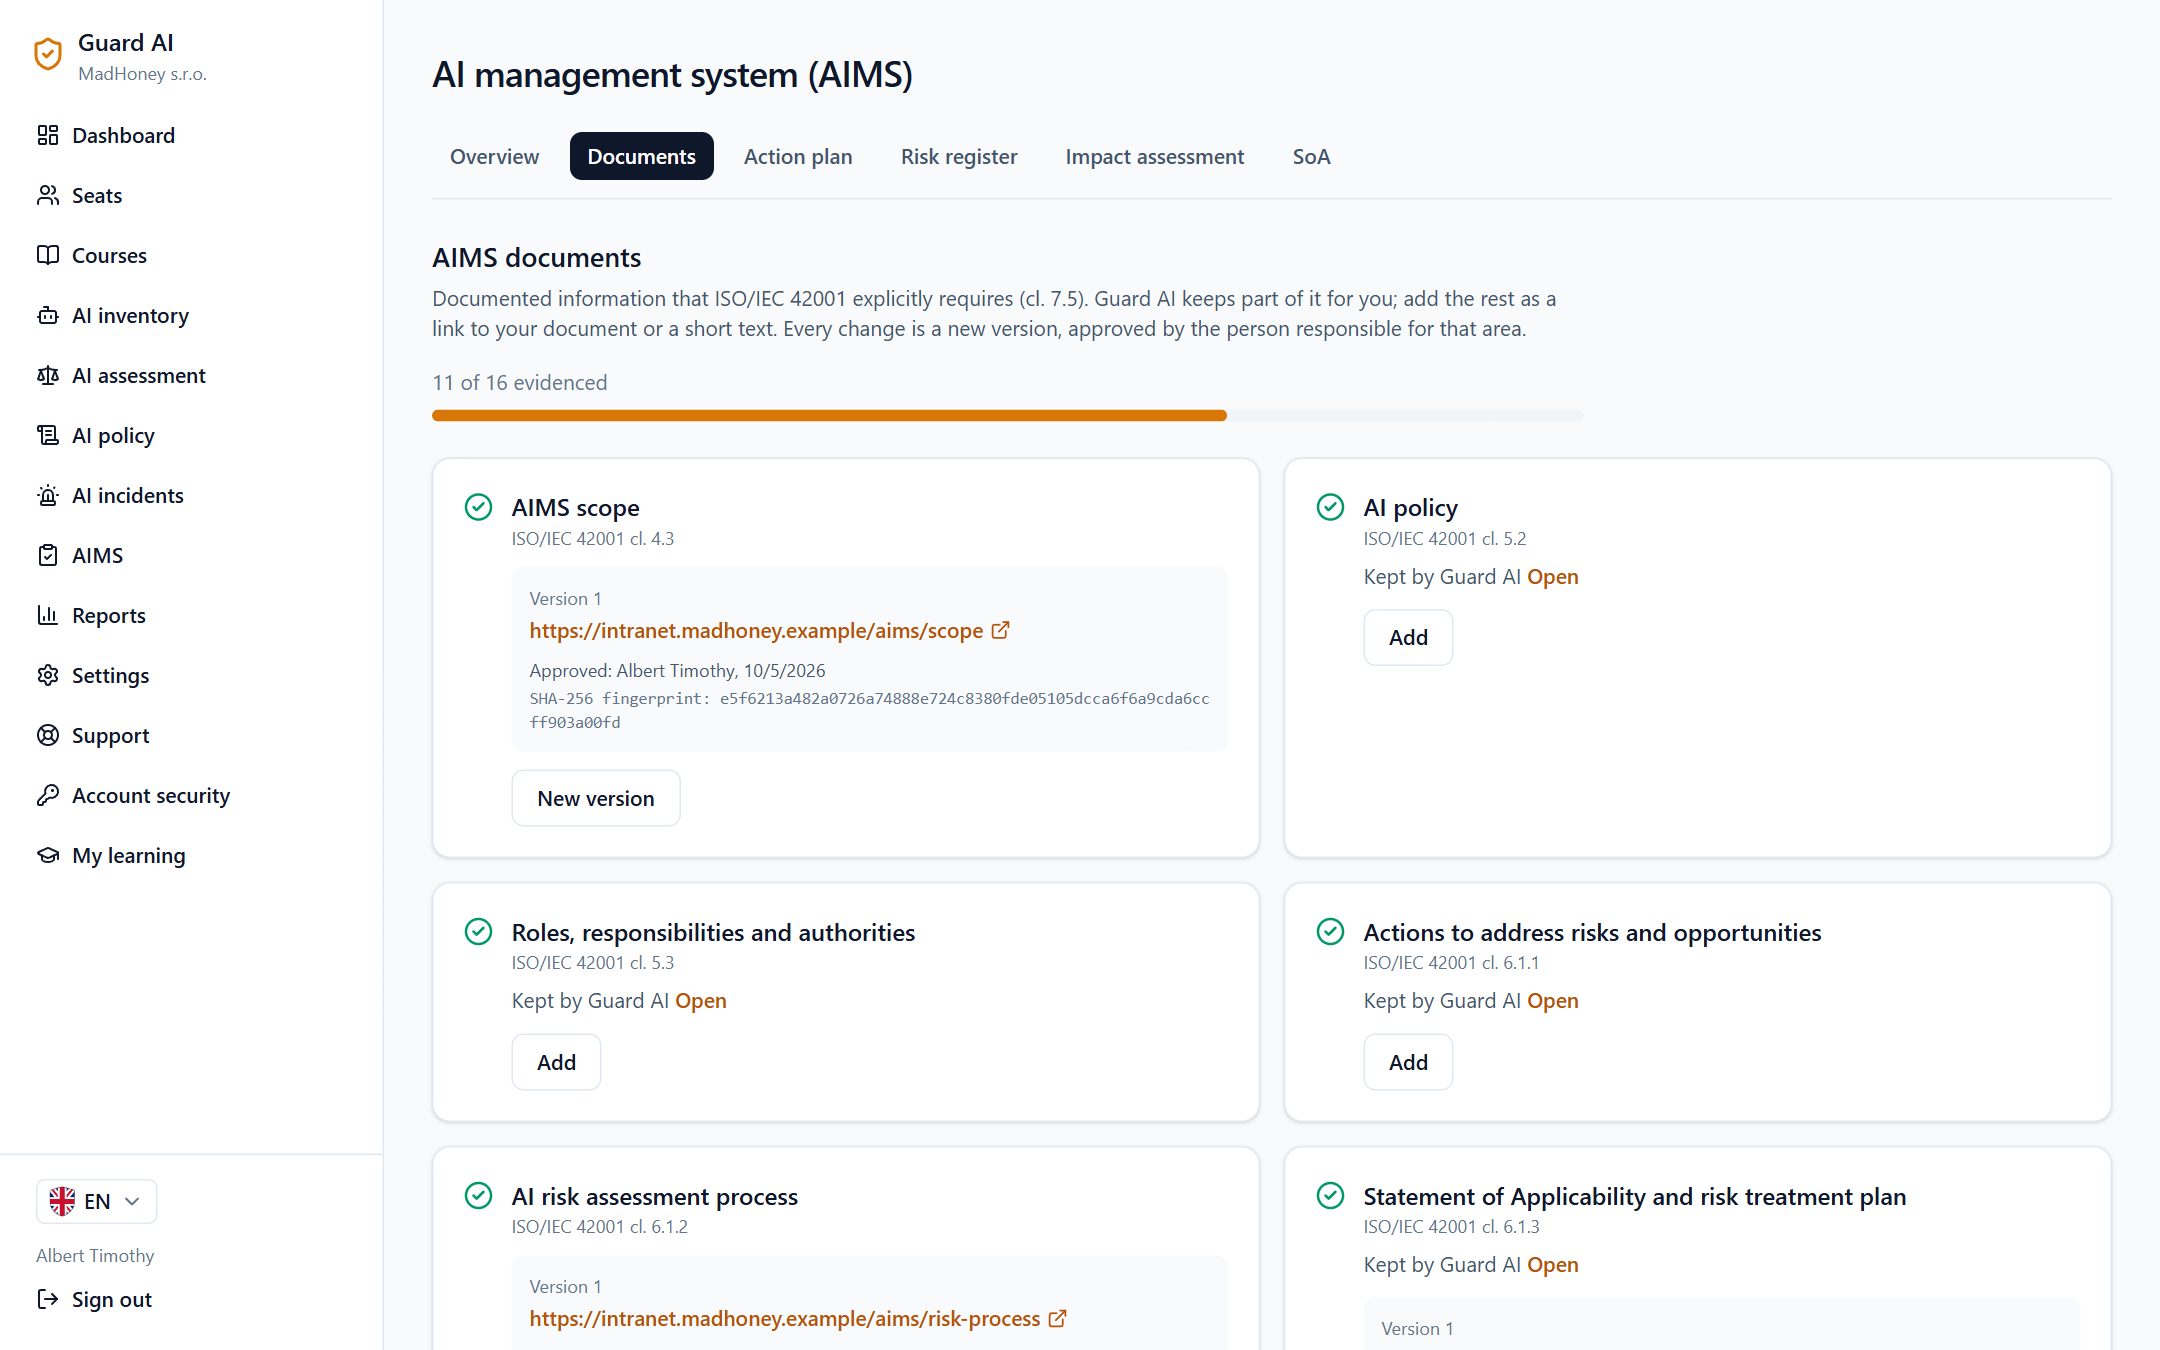
AIMS documents with approval

Sixteen pieces of documented information the standard requires. Guard AI fills in what it already records; you add the rest as a link or text. Each version is approved by the responsible person, with the time and a SHA-256 fingerprint stored.

  • In every plan
  • AIMS role holders approve too, not only admins
  • Action plan with reminders and calendar export
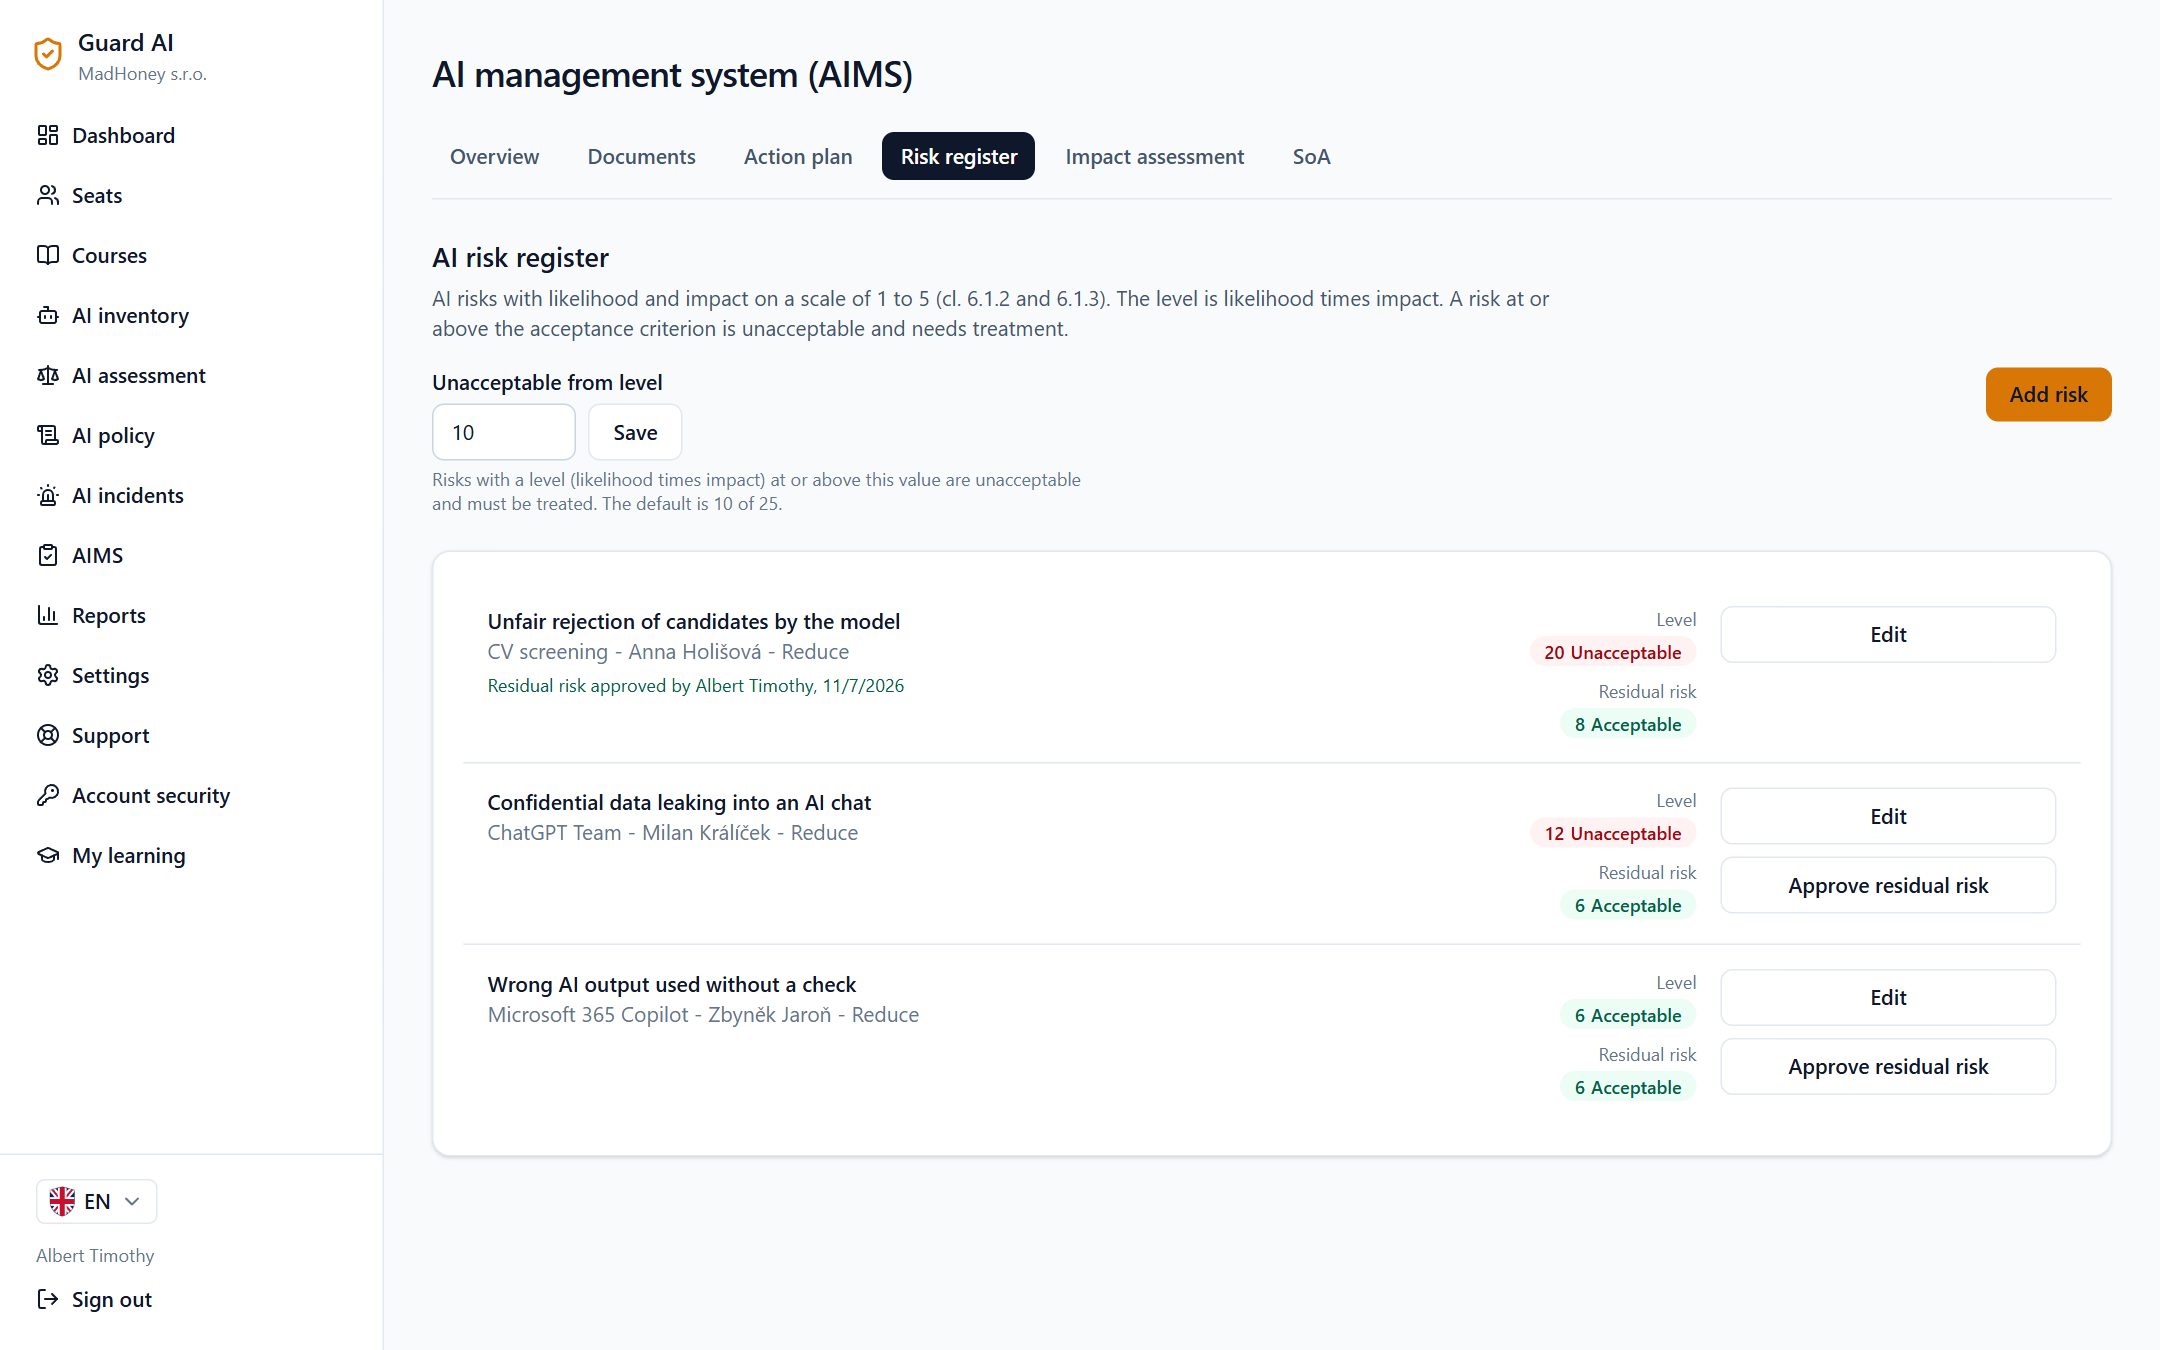
AIMS documents with versions and approval

Risk register and impact assessment

AI risks with likelihood and impact, your own acceptance criterion and approval of the residual risk. Plus impact assessments of AI systems on people and society.

  • In every plan
  • Unacceptable risks are highlighted and on top
  • Link a risk to an action in the plan
  • Statement of Applicability (SoA) for the 38 Annex A controls, print and CSV for auditors
AI risk register with level and residual risk

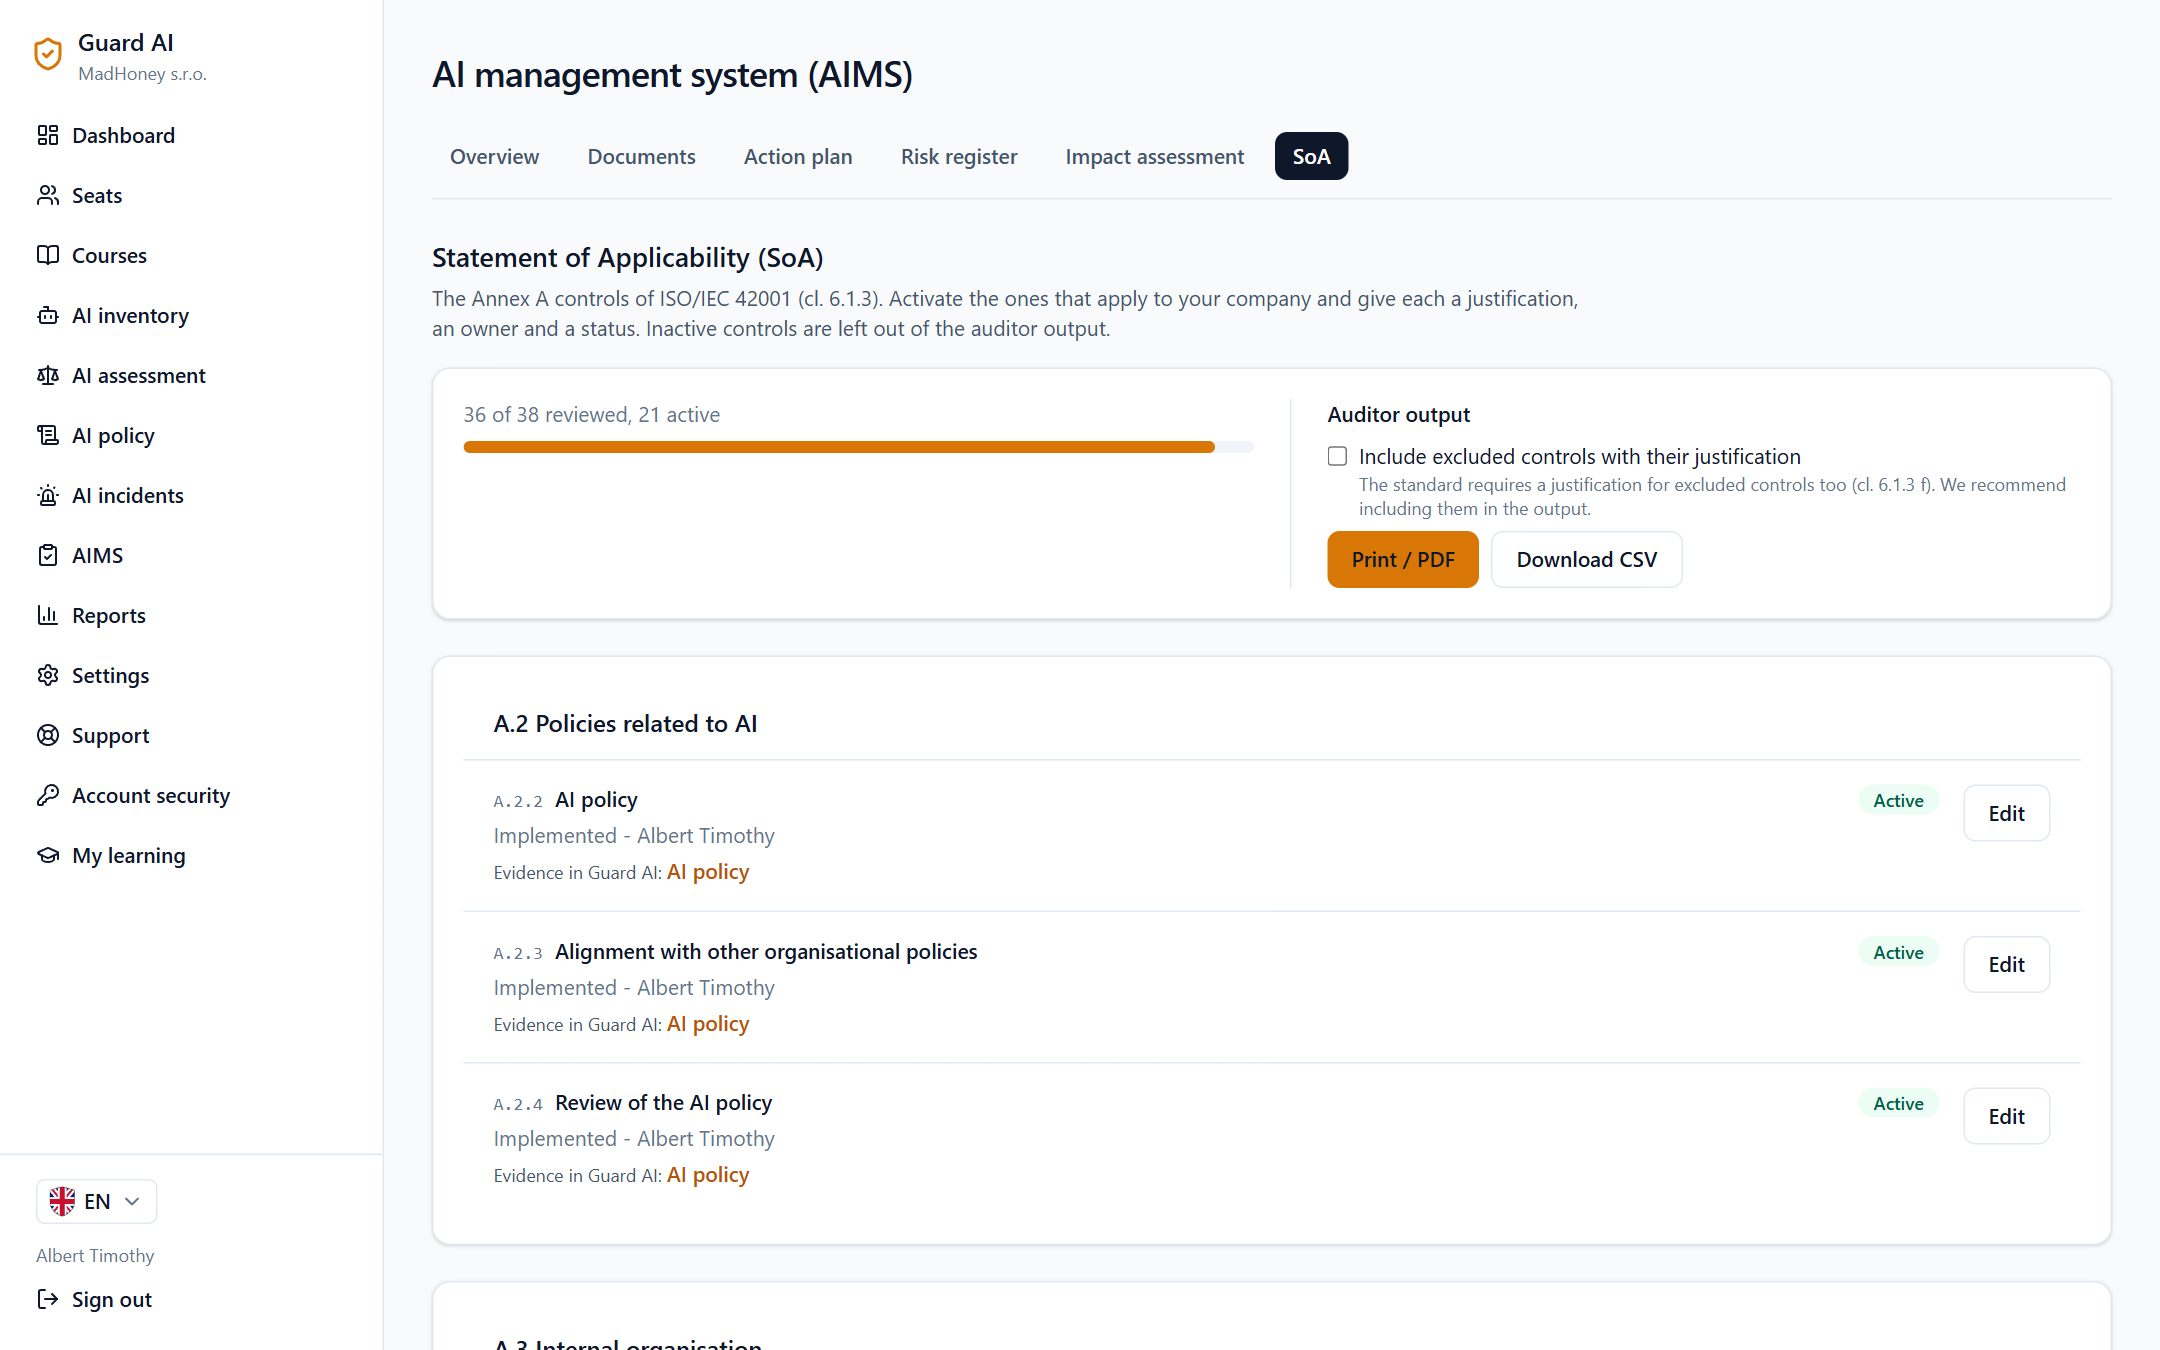
Statement of Applicability (SoA)

All 38 Annex A controls of ISO/IEC 42001. Activate the ones that apply, add a justification, an owner and a status. Where Guard AI already holds evidence, the control links to it.

  • In every plan
  • Auditor output to print, save as PDF or download as CSV
  • Excluded controls with justification on request
Statement of Applicability with the Annex A controls

What the auditor gets

  • The Statement of Applicability with the active controls, and on request the excluded ones with their justification
  • AIMS documents with version, approver name, date and SHA-256 fingerprint
  • The risk register with approved residual risks and the impact assessments
  • Separately: the audit proof pack as PDF with training, policy, inventory and incidents, verifiable at guard-ai.eu/verify

In every plan

  • AIMS readiness checklist
  • Roles and responsibilities with contact people
  • Documents with approval
  • Action plan with reminders
  • Incident reporting, including anonymous reports
  • AI risk register with an acceptance criterion
  • AI system impact assessment
  • Statement of Applicability with an auditor output
See pricing

AIMS questions

Is this an ISO/IEC 42001 certification?
No. Guard AI helps you prepare, run and evidence an AIMS. A certification body issues the certificate after its own audit.
Do we need to be certified to use the AIMS in Guard AI?
No. You can run an AIMS as an internal AI management system without certification. If you decide to get certified, the material is already there.
We only use AI, we do not develop it. Is this for us?
Yes. In the Statement of Applicability you exclude the development-focused controls with a justification. The rest, meaning rules, people, suppliers, risks and incidents, applies to companies that only use AI too.
Where are our documents stored?
You add documents as a link to your own storage, such as SharePoint or Google Drive, or as a short text. We do not store files.
Comply before someone else checks

Pick your team size and get started today.

Go to pricing